Attackers exploited internet-facing Palo Alto Networks management interfaces, then used compromised firewalls to reach internal identity infrastructure. The campaign combined the PHP2Shell vulnerabilities with a separate Linux kernel flaw. Recovered artifacts document 25 compromised firewall and management servers, including three systems in a US government-affiliated environment.
Palo Alto Networks has confirmed active exploitation against exposed PAN-OS management interfaces. Its October 29 update also confirms independent verification of the campaign’s tooling and reported results. However, the evidence does not establish that every attempted directory attack succeeded or identify a government sponsor.
The Management Interface Was The Entry Point
PHP2Shell covers CVE-2026-109618 and CVE-2026-109619, two PHP runtime vulnerabilities rated 9.2 under CVSS 4.0. Both can enable code execution without credentials under the required conditions. On affected appliances, the exposed administrative web service provided the route into that runtime.
The affected surface includes the HTTPS management interface and XML API service on PAN-OS and Panorama. A dataplane interface is affected only when it has a management profile attached. Therefore, an internet-facing firewall does not automatically imply an internet-facing administration service.
The official advisory explicitly excludes GlobalProtect portal, gateway and Clientless VPN from this issue. Although the technical report describes shared web-server infrastructure, that does not make those VPN services vulnerable entry points. Internal VPN infrastructure later appeared among the destinations reachable through the attacker’s tunnel.
Memory Exhaustion Became Command Execution
The PHP flaws interrupt the runtime’s handling of memory and fatal errors. With CVE-2026-109618, an out-of-memory failure can leave partially initialized data behind. Cleanup may later treat that invalid state as usable memory.
CVE-2026-109619 concerns stale global state that still points into memory from a previous request. When the same worker handles another request, it can access memory that PHP has already freed. Together, these conditions give an attacker ways to influence what the runtime reads or executes.
In the recovered exploit, crafted multipart requests targeted PHP’s session.upload_progress handling in the management web server. Memory pressure prepared the process for corruption. A subsequent out-of-bounds read exposed a library pointer through a Set-Cookie response, allowing the attacker to determine the loaded PHP library’s location.
Another memory-exhaustion stage left a stale session reference. The final stage forged a HashTable entry in freed memory and redirected its cleanup callback to PHP’s system() function. As a result, normal cleanup executed an attacker-supplied command as the nobody service account.
This required several coordinated request stages. References to a single request concern the final stage that joins command execution to privilege escalation, rather than the entire preparation sequence.
A Kernel Flaw Lifted The Service Account To Root
Initial PHP execution did not itself provide unrestricted system control. The service account operated under SELinux restrictions that limited changes to system files. Consequently, the attacker added Fragnesia, tracked as CVE-2026-46300, to cross that second boundary.
This Linux kernel flaw affects the XFRM ESP-in-TCP subsystem. The recovered chain used page-cache writes to alter the authentication policy consumed by su. After that change, the account could obtain root access without a password.
Root privileges then allowed the attacker to plant a PHP webshell and verify its effective identity. However, the exploit depended on precise memory layouts for particular software builds. Recovered version profiles included both tested configurations and provisional calculations, so their presence does not establish successful exploitation of every listed build.
The Firewall Opened A Route To Its Management Server
The campaign’s discovery list contained approximately 19,000 internet-facing devices. Version and geographic filtering narrowed the working target list to 240 systems in the United States, Japan, Taiwan and South Korea. These discovery and targeting counts are separate from confirmed compromises.
The report distinguishes 24 compromised perimeter firewalls from a subsequently compromised internal management server, producing the total of 25 systems. For 22 firewalls, recovered evidence showed a planted webshell without further observed activity. Two perimeter devices drew deeper attention because they appeared connected to one US government-affiliated environment.
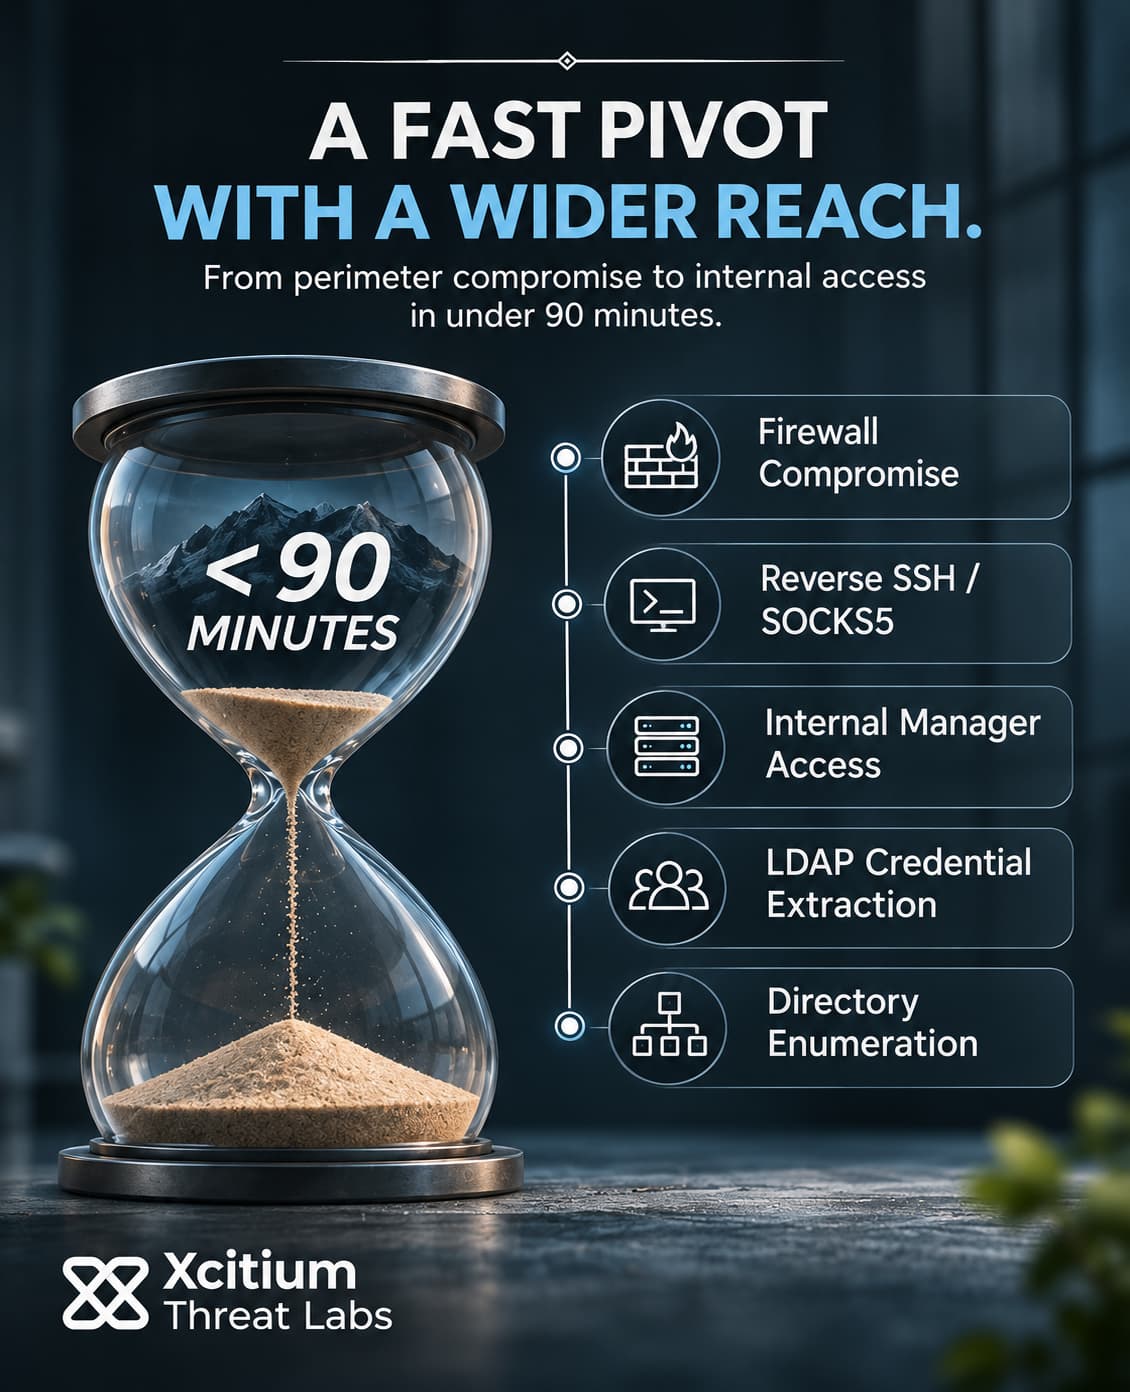
After the first device crashed, the attacker successfully compromised the second on October 24. Its reverse SSH tunnel exposed internal services through the perimeter foothold. An accompanying SOCKS5 proxy provided broader internal connectivity, while startup mechanisms supported reconnection after reboot.
Less than 90 minutes later, the same PHP and kernel exploit chain reached the internal firewall management server through that tunnel. Central administration therefore expanded the breach beyond the original appliance to stored configurations, credentials and network settings.
Stored Credentials Connected The Breach To Active Directory
The management server already had LDAP connectivity to Active Directory. Its configuration contained an encrypted service-account password, but root access also exposed the material needed to decrypt it. The attacker recovered that credential and used directory queries to enumerate users and groups.
Further scripts attempted password spraying, account creation and extraction of an identity provider’s signing key. However, their result files remained outside the recovered evidence. Credential extraction and directory enumeration are confirmed; successful backdoor accounts, stolen signing keys and domain takeover are not.
Chinese-language activity and other operational indicators support a suspected China nexus. They do not establish a named group or state sponsor. Similarly, installed AI tools do not prove that an autonomous agent developed or ran the operation.
Patch Availability Is Separate From Intrusion Scope
By the November 2 review, the official advisory listed released fixes across the affected PAN-OS 10.2, 11.1, 11.2, 12.1 and 12.2 branches. Its release history records hotfix availability, although generic solution wording still refers to upcoming releases. Those records establish available corrections, rather than their deployment on any particular device.
We previously examined PHP2Shell virtual patching for hosting environments. This campaign adds a different operational consequence. Once a vulnerable administration service yielded root access, the attacker could reuse the appliance’s internal routes and stored secrets. A corrected software build interrupts that exploit chain; it does not, by itself, establish what happened to credentials or internal systems before the update.
Conclusion: The Management Server Held The Next Credential
The decisive failure extended beyond remote code execution on a firewall. An exposed management service gave the attacker a foothold, while a separate kernel exploit supplied root privileges. From there, existing network routes and stored credentials connected the compromised appliance to systems deeper inside the organization.
The internal management server increased that reach because it held configurations and could communicate with Active Directory. Encryption protected its stored service password only until the attacker obtained the material needed to decrypt it. Consequently, the same infrastructure that supported routine administration also supplied a path for directory reconnaissance.
Confirmed credential extraction and enumeration justify investigating that path. However, attempted account creation and signing-key theft remain unresolved. Recovery must test those possibilities without presenting them as established domain takeover.
Why This Threat Matters
- Administration creates a separate exposure. A firewall’s public traffic function does not require its management service to accept internet connections.
- Privileges accumulate across flaws. PHP execution supplied the starting account; the kernel vulnerability enabled system-level changes.
- Central management expands investigative scope. Access to a management server exposes configurations and secrets for systems beyond the initial device.
- Stored encryption has an access boundary. Root access allowed the attacker to recover the directory service credential in this case.
- Updates and recovery answer different questions. A corrected build addresses the vulnerability, while investigation establishes what earlier access enabled.
Where Defensive Control Must Operate
Xcitium Vulnerability Assessment supports discovery and prioritization of external exposure through assessment of firewall configurations, open ports, internet-facing services and outdated software. Here, the relevant finding is a reachable administration service on an affected device. Remediation must then match the installed appliance build to the appropriate vendor correction and verify that management access follows the intended restrictions.
Incident investigation must also follow the routes available from the compromised firewall. Correlating device activity with management-server and directory records can establish whether the exposed account reached additional resources. Such analysis depends on available telemetry; an assessment report alone cannot demonstrate that a webshell, tunnel or unauthorized account has disappeared.
Restore The Management Path Before Renewing Its Secrets
Remove public access to administration and restrict the compromised device’s internal reach as part of the response. Preserve relevant logs, configurations and volatile evidence before disruptive recovery actions. Then investigate the internal manager and directory activity, including unauthorized accounts, privilege changes and continued tunneling.
Restrict exposed account access during recovery, taking the services that depend on it into account.
Restore affected systems through a trusted recovery process before introducing replacement credentials. Rotate the exposed directory service password, review its permissions and determine which other accessible secrets require renewal. Finally, verify that authorized administration still works and that the recovered devices cannot recreate the attacker’s internal access path.