A Java service can corrupt its own memory while it reads data from a request that has yet to pass authentication. Java4Shell, tracked as CVE-2026-114938, affects the optimized Base64 decoder in OpenJDK. On an affected deployment, the flaw can crash the service. Under certain conditions, it can also allow remote code execution with the Java process’s permissions.
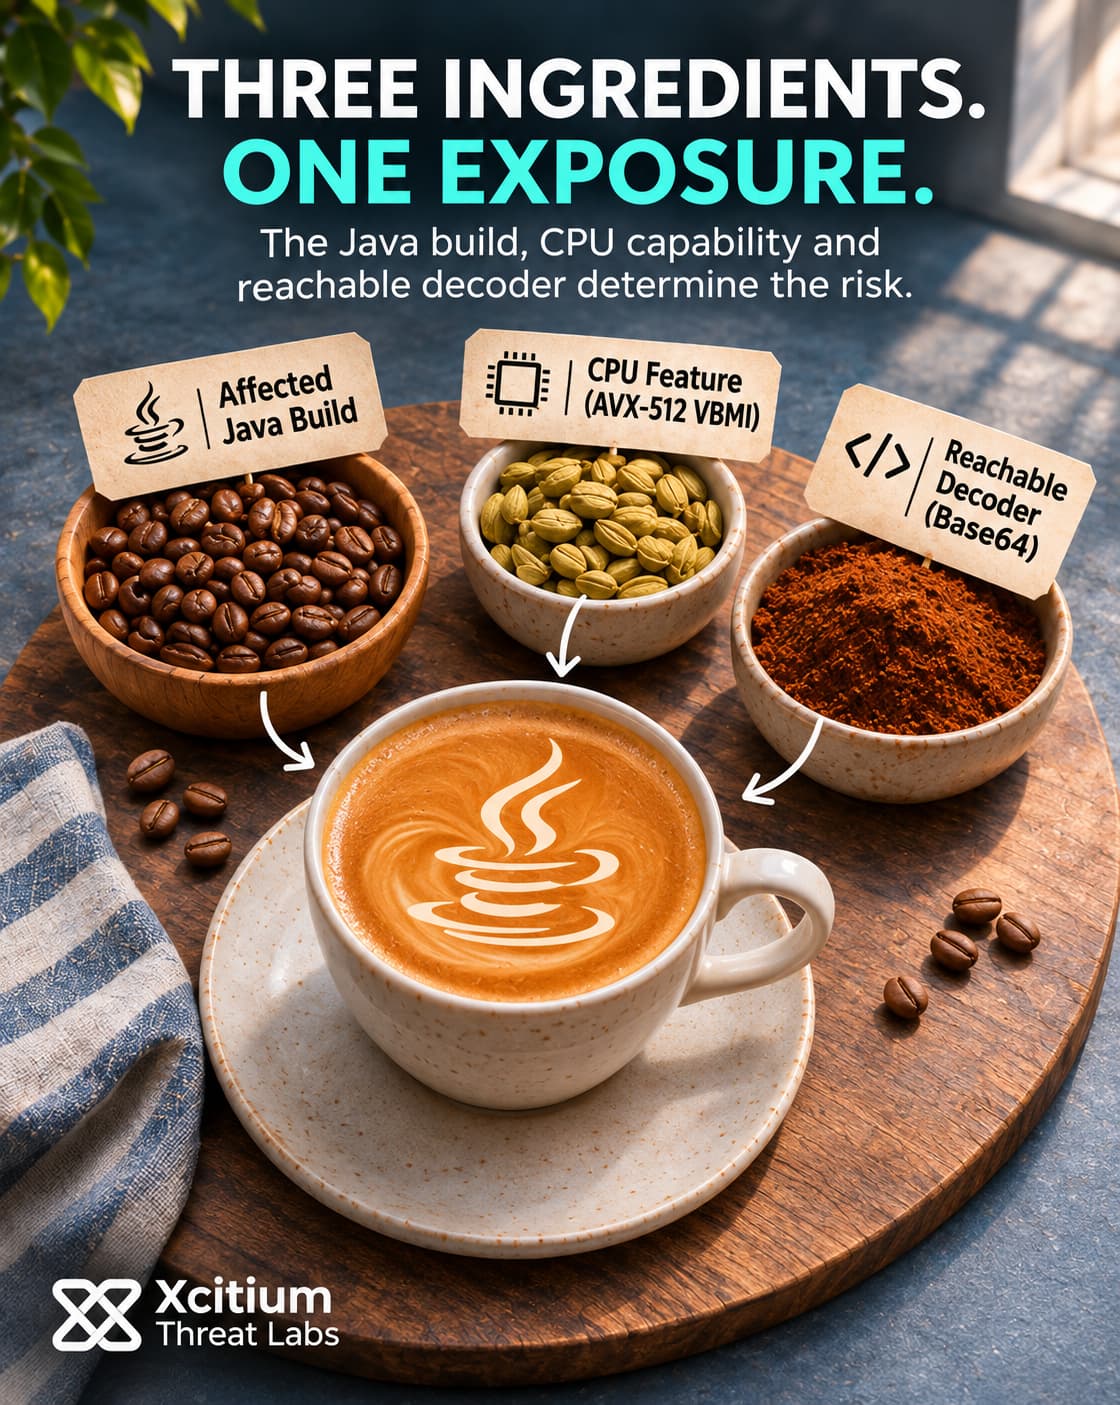
The same runtime flaw reached identity services, build servers and collaboration tools in controlled tests. However, exposure depends on three things coming together. The service must run an affected Java build, its processor must support the vulnerable optimization, and external input must reach that decoder. A login page alone tells an operator little about the order in which those checks happen.
A Faster Decoder Writes Beyond Its Buffer
Base64 represents binary data as text. Applications routinely decode credentials or protocol fields before they can interpret them. OpenJDK supplies a standard decoder for that work, so unrelated Java applications can inherit the same flaw from the runtime. They may use that decoder directly or reach it through another component.
On supported processors, the HotSpot just-in-time compiler can select an intrinsic, a specialized native routine it uses in place of the ordinary Java implementation. The routine processes several bytes at once. However, the affected implementation can write past the end of the allocated output buffer when it handles malformed data. That write can damage neighboring memory within the same process.
Once that boundary fails, the result depends on what the application does with the damaged data. A crash is one possible result. Controlled demonstrations also showed that memory corruption could lead to disclosure or code execution. Consequently, the initial memory error and a successful takeover are separate findings. The latter depends on how the individual application handles requests and uses memory.
Authentication Can Come After Decoding
Some services need to decode part of a request before they can decide whether to accept it. For example, HTTP Basic authentication represents credentials as Base64 text. A service that uses the affected Java decoder to read that field can reach the vulnerable routine before checking the credentials.
Keycloak, Jira, Confluence, Jenkins, JFrog Artifactory and PingFederate all showed pre-authentication code execution in tested default setups. However, those results still depended on a vulnerable runtime and compatible hardware. Other tested products exposed the relevant processing only after login. For example, the Apache Kafka Broker and Apache Solr demonstrations required authentication.
This distinction matters when two teams run the same application release. One may use a bundled runtime inside a container, while another uses a Java installation on the host. Also, each deployment can expose a different set of interfaces. For inventory purposes, start with the application name. Actual exposure depends on the running Java build and which inputs reach it.
Hardware Narrows the Affected Fleet
The affected optimization uses AVX-512 VBMI on x86-64. That feature is available on supported processors such as Intel Xeon Ice Lake and AMD Zen 4 or newer. However, a virtual machine must also see the required CPU features. Identical software images can therefore have different exposure on different nodes. ARM64 runs outside the affected x86-64 path.
The affected OpenJDK 17 line begins at 17.0.6, and vulnerable builds also exist in the 21, 25 and 27 lines. Oracle lists a separate Java 8 Performance Pack build and specific GraalVM releases. As a result, a fleet inventory that records only the Java major version can hide both an affected vendor build and a backported fix.
Oracle and OpenJDK released fixes on November 17, 2026. Fixed upstream versions include 17.0.21.1, 21.0.13.1, 25.0.5.1 and 27.0.1.1. Distribution and application vendors publish their own builds. Likewise, an updated host package can coexist with an older bundled runtime until the application or image also changes.
Reported Attempts Leave the Outcome Open
A reported Java4Shell attempt used a request that identified itself as Chrome. In a separate observation, telemetry associated Java4Shell and ARTEX traffic with the same source address. However, the public account did not confirm that ARTEX produced the Chrome-labeled request or that either observation resulted in compromise.
Those observations capture activity at the web layer. Evidence of what happened inside a targeted service would come from a different set of records, such as application errors, JVM crashes or unexpected activity from the Java process. In practice, an investigation needs both views to distinguish an incoming attempt from its effect.
Conclusion: The Fix Has to Reach the Running JVM
Java4Shell puts the request boundary ahead of the login boundary. On an affected Java service, the runtime can decode data supplied by the caller before the application decides whether to trust that caller. That ordering lets a memory error occur during a request the service would otherwise reject. As a result, the vulnerable operation can run before the login gate takes effect.
Exposure can differ across a fleet. The Java build and the CPU features available to the JVM determine whether the vulnerable optimization can run. Meanwhile, the application determines which data it passes to the decoder. Controlled tests demonstrated code execution on some deployments. In the field, reports documented attempts whose outcomes remain unknown. That distinction matters when teams decide which systems to patch and which records to preserve.
Why This Threat Matters
- Shared runtime. Identity, build and collaboration services can inherit the same flaw even when separate teams maintain those applications.
- Processing before login. Some requests reach the decoder before credential validation, so access reviews must account for unauthenticated traffic.
- Node-specific exposure. Two replicas can run the same image while their hosts expose different CPU features to Java.
- Bundled Java. A service can keep using the runtime in its own image or installation after the host’s Java package changes.
- Separate evidence. Request logs can document an attempt. Process and application records help determine whether the service crashed or showed unexpected behavior.
Where Defensive Control Must Operate
Xcitium Vulnerability Assessment helps identify exposed services and outdated software across internet-facing infrastructure. Use those findings to prioritize reachable Java services, then pair them with deployment records that show which runtime each service uses. That gives platform teams a way to rank work by both network exposure and the state of the running application.
Verify Every Instance After the Rollout
Apply the vendor’s fix to the runtime the service actually uses. For bundled deployments, that can mean rebuilding or replacing the application image, then rolling it out. Where patching must wait, use the vendor-documented option to disable the affected Base64 optimization and verify the effective setting after restart. Finally, check every replica and failover node that can serve requests. A rollout is complete when each serving instance has a fixed runtime or a verified interim mitigation. Track mitigated instances until the permanent update reaches them.