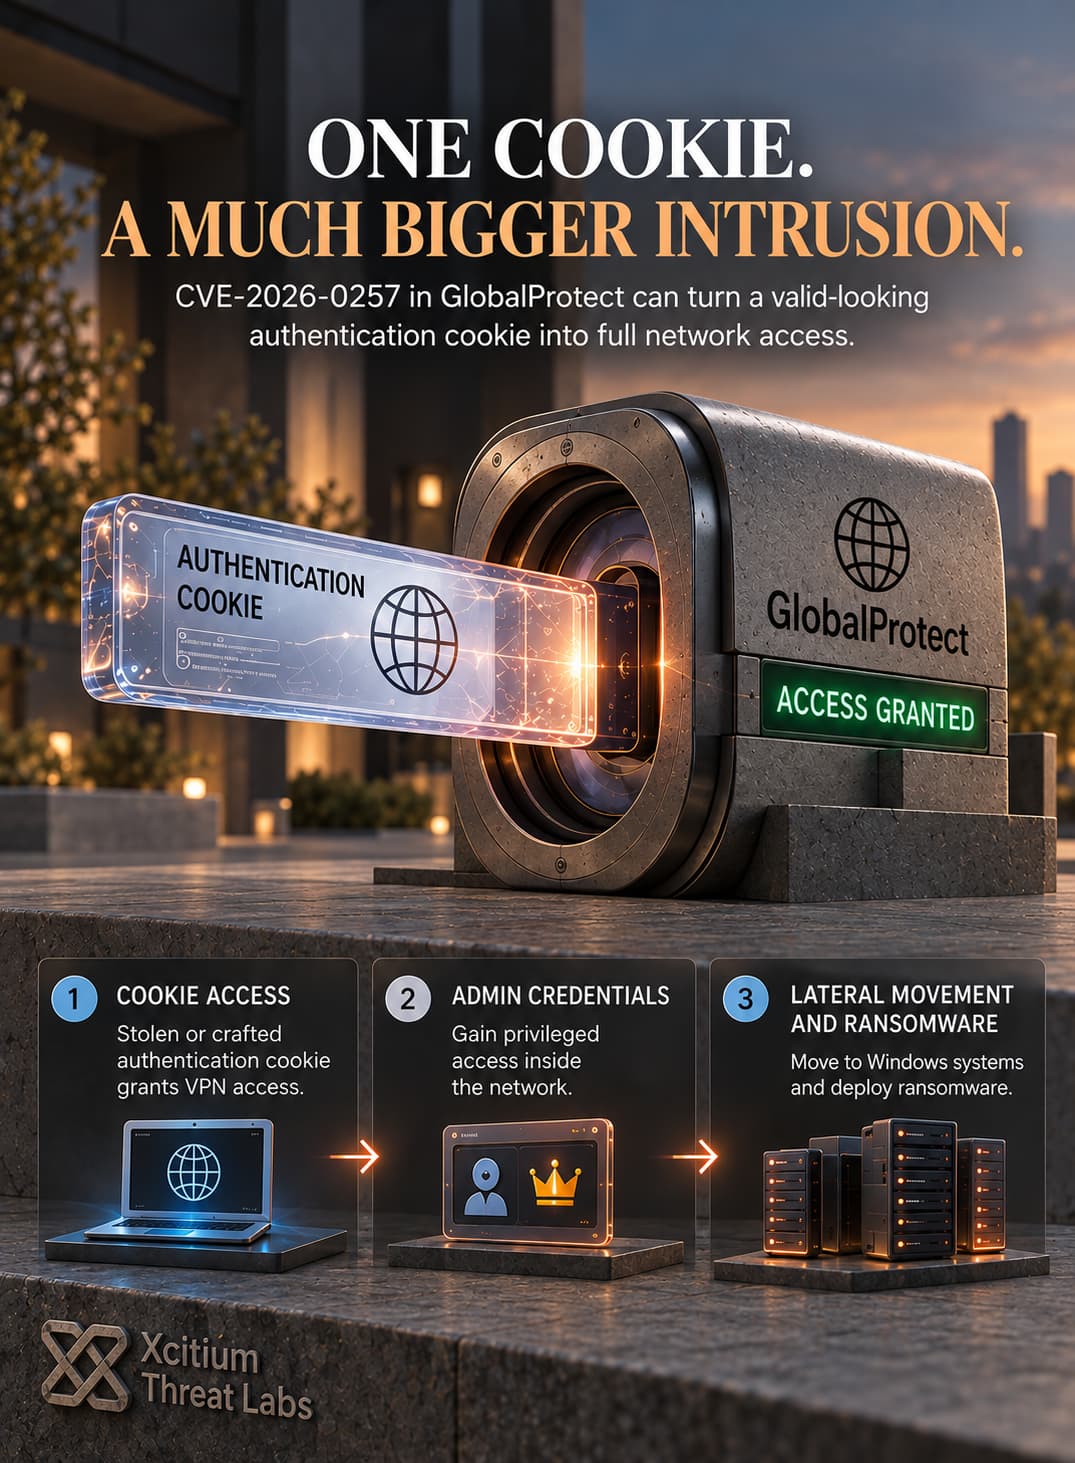
Ransomware operators are exploiting CVE-2026-0257 to enter corporate networks through GlobalProtect, then pursue systems beyond the VPN gateway. An October 19, 2026 update identifies activity involving Qilin and Inc, while separate public reporting links exploitation to actors using Settra. The flaw lets attackers establish unauthorized VPN connections under specific configurations.
After the connection succeeds, an intruder can search for credentials, administrative access and systems holding business data. Consequently, the VPN event can mark the beginning of a much larger intrusion rather than its final impact.
Authentication Cookies Become An Entry Point
The vulnerability affects the GlobalProtect portal and gateway in PAN-OS, with affected releases also listed for Prisma Access. Exposure requires authentication override cookies and a particular certificate configuration. Therefore, an internet-facing GlobalProtect service alone does not establish that a deployment is vulnerable.
Authentication override cookies let an earlier authentication carry forward without repeating the full sign-in process. However, the vulnerable implementation can accept a cookie that gives an attacker unauthorized access. The current advisory rates the issue 7.8, High, with the highest suggested urgency.
That distinction separates this flaw from an exploit that immediately runs commands on a firewall. Here, the documented initial result is a VPN connection. Any later credential theft, remote execution or encryption requires additional activity after entry.
May Access And October Activity Are Separate Evidence
The security advisory dates to May 13, 2026. Successful exploitation observations reach back to May 17, followed by another wave on May 21. In those early cases, cookie authentication led to internal VPN address assignment, although the investigation did not identify subsequent lateral movement.
Those observations establish access, not a completed ransomware attack. They also describe a particular investigation window; an absence of follow-on activity there cannot establish what happened in later intrusions.
Meanwhile, CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on May 29, with a June 1 remediation deadline for covered federal agencies. The current catalog also records known ransomware use. October’s reporting therefore concerns continued criminal exploitation of a previously disclosed weakness, rather than a newly announced zero-day.
Administrative Credentials Expand The Intrusion
Separate investigations into June 2026 intrusions documented Qilin encryption after exploitation of the same flaw. Attackers harvested credentials from LSASS memory and extracted the Active Directory database. They then used compromised administrative accounts to reach other Windows systems.
Remote execution relied heavily on PsExec and administrative shares, with RDP providing another route. Some cases also included remote access software that gave attackers alternative connections. As a result, continued access no longer depended entirely on the original VPN session.
This progression changes the meaning of an apparently ordinary administrative action. A remote file transfer or service launch may use a valid account, yet still belong to the intrusion. The account’s permissions explain why the action succeeds; they do not establish that its operator is legitimate. Likewise, a familiar administration utility does not explain who authorized its use.
One Intrusion Reached The Virtualization Layer
The October update describes one case in which attackers pivoted from the compromised VPN gateway to vCenter. They disabled the execInstalledOnly control on ESXi hosts, then used a custom tool to extract credentials offline from a domain controller’s VMDK virtual disk.
Because that extraction targeted the virtual disk, it bypassed security controls and EDR operating inside the guest system. This is a different execution location from a credential dumper running within Windows. The observation does not show that every affected network suffered the same pivot.
However, it illustrates why a quiet guest operating system cannot describe all activity against its data. The relevant action may occur through the infrastructure managing that guest. Access to the virtualization platform changes what an intruder can reach without entering the usual process path inside a virtual machine.
Encryption Followed Different Paths Across Victims
The June cases did not all follow an identical sequence. Some progressed to encryption without observed data exfiltration, while others included data theft before ransomware deployment. Such variation is consistent with different affiliates using a shared ransomware service, although it does not establish their identities.
Attackers also cleared Windows event logs and used password-gated ransomware payloads. Without the required runtime password, those payloads remained inactive, complicating analysis. Consequently, an executable’s behavior outside its original launch conditions may fail to reveal the behavior it performed during the intrusion.
The evidence therefore supports several outcomes from the same initial weakness. It does not support assigning data theft to every victim, or treating every successful VPN session as proof that encryption followed.
Fixed Software Does Not Describe Earlier Access
The advisory lists fixes across multiple PAN-OS release branches. For example, its 11.1 branch includes 11.1.13-h5 and 11.1.15, depending on the starting release. However, a fixed version appearing in that table proves availability, not installation across customer environments.
The fix also changes how authentication override cookies work and requires users to authenticate again after upgrading. That software change is distinct from the historical question of whether an attacker already obtained internal credentials. Earlier access, subsequent account use and current software status describe different parts of the same investigation.
Conclusion: VPN Access Must Not Become Infrastructure Control
Exploitation of CVE-2026-0257 breaks the trust decision that admits a remote connection to the corporate network. In an affected configuration, an authentication override cookie can establish unauthorized VPN access. That access gives the intruder a position from which to pursue additional privileges. It does not itself establish command execution on the firewall or prove that ransomware followed every connection.
Subsequent intrusions demonstrate how that foothold can expand. Attackers used stolen administrative credentials to move across Windows systems and deploy ransomware. However, one investigation also traced a pivot into vCenter and offline credential extraction from a domain controller’s VMDK. Because the extraction occurred outside the guest operating system, endpoint visibility inside that guest could not cover the action against its disk.
Why This Threat Matters
- Configuration determines exposure. An exposed portal alone does not prove vulnerability, so remediation must verify cookie settings, certificate use and the installed release.
- Administrative access carries attacker intent. Valid accounts and familiar tools can support hostile remote execution, making the operator’s authorization as important as the executable’s reputation.
- Virtualization changes the observation point. A quiet domain controller cannot establish that its virtual disk remains untouched when attackers control the management infrastructure.
- Victim outcomes differ. Encryption occurred with and without observed data theft, so investigators must establish each impact independently.
- Alternative access can survive patching. Additional remote access software gives intruders another route, even after the original VPN weakness closes.
Where Defensive Control Must Operate
Xcitium Advanced EDR, powered by Xcitium’s patented Zero-Dwell platform, addresses malicious execution on supported, managed Windows endpoints. Its telemetry supports investigation when suspicious processes lead to ransomware activity. Execution Governance restricts unknown code’s access to real system resources before trust is established. Here, that control belongs at the endpoint payload stage, where an intruder attempts to turn network access into executable activity.
Xcitium Vulnerability Assessment supports the perimeter exposure review through external service inventory, vulnerability assessment and remediation guidance. However, administrators must still verify this flaw’s specific configuration requirements and the correct fixed release. A general assessment capability does not establish a verified detection check for this particular vulnerability.
These controls complement gateway remediation and privileged access restrictions. A legitimate administration utility still requires authorization review, while offline virtual disk access requires scrutiny at the virtualization layer. An endpoint agent inside a guest cannot substitute for controls over the infrastructure managing it.
Validate Recovery Beyond the Gateway
Recovery should connect the original VPN session to everything it could reach. Preserve gateway records, correlate suspicious sessions with administrative logons and remote service activity, and inspect newly introduced remote access software. Separately review vCenter access and ESXi control changes, including execInstalledOnly. Where evidence shows credential exposure, revoke affected access and plan credential recovery across the implicated systems. Finally, verify the fixed configuration across all relevant portals and gateways. Closing the entry point and removing access already established inside the network require separate evidence.