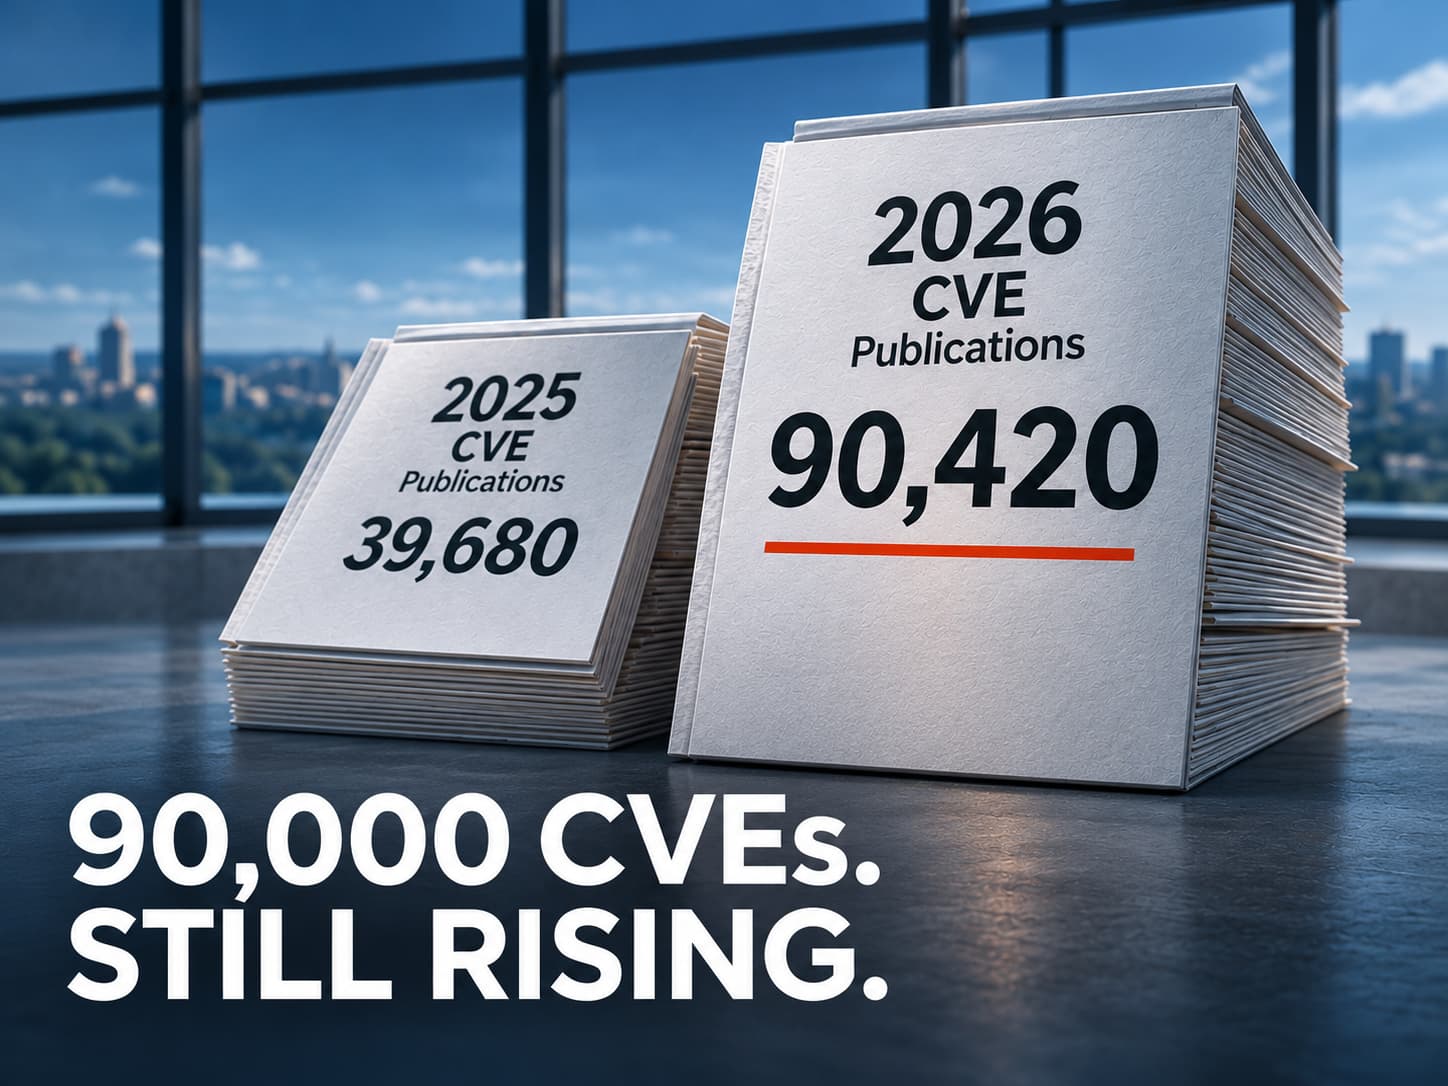
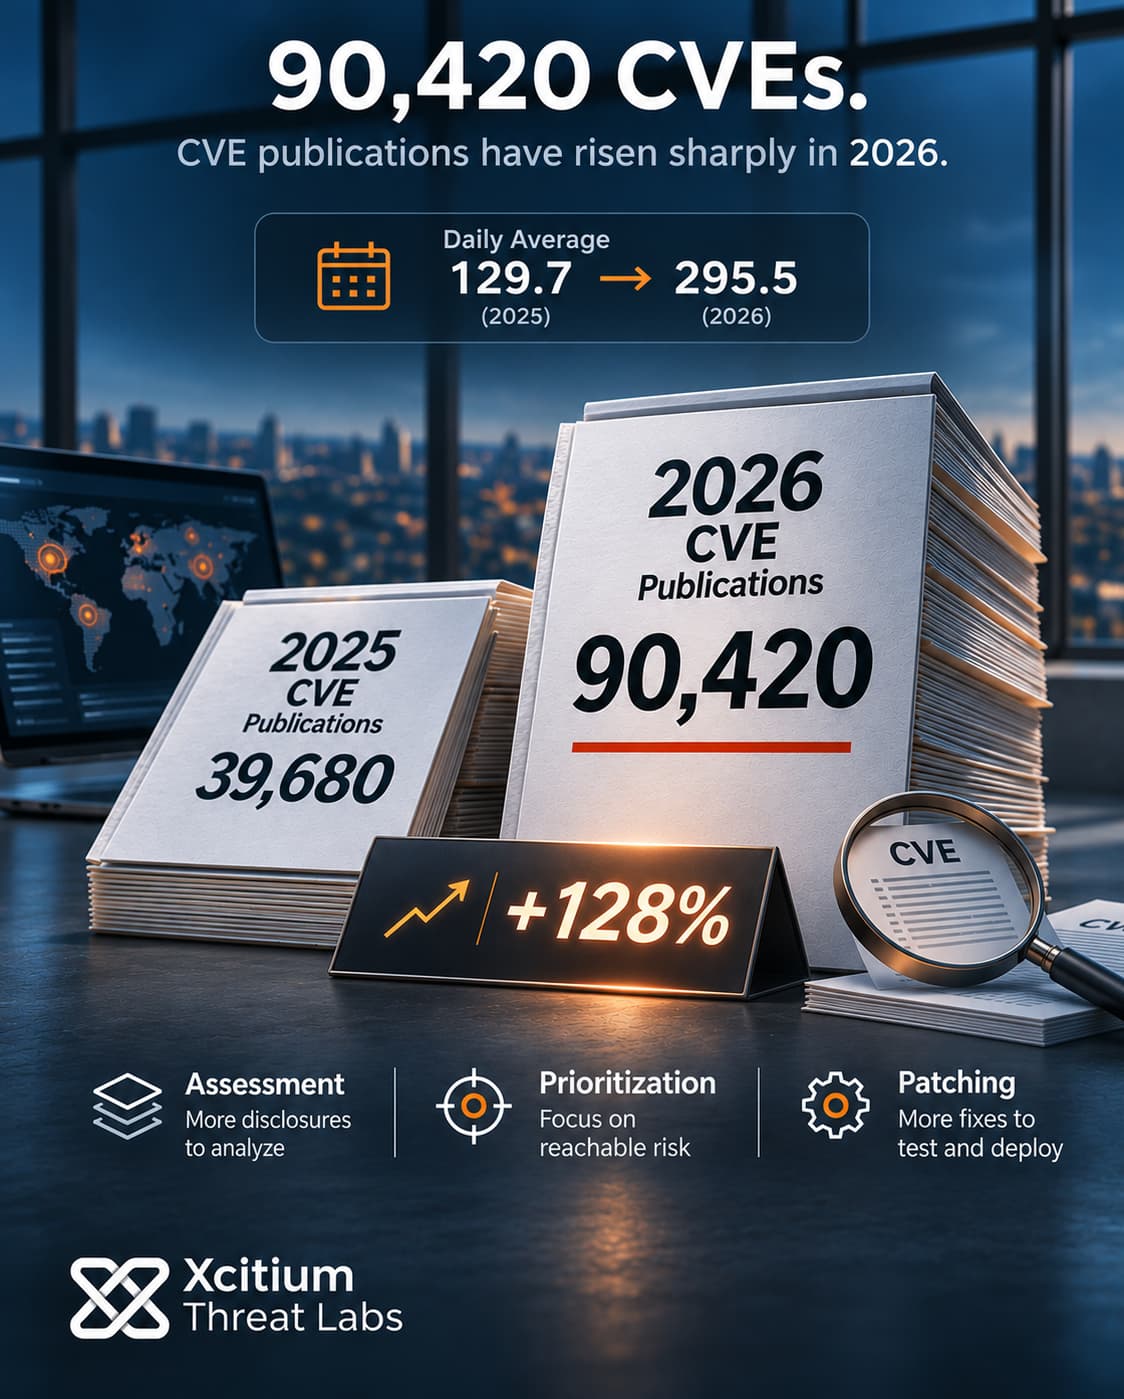
CVE publications have passed 90,000 in 2026, putting more assessment work into vulnerability management queues before the year ends. By November 3, the total stood at 90,452, compared with 48,151 across all of 2025. This increase creates pressure wherever teams must connect new disclosures to affected software, exposed services and available fixes.
The term Vulnpocalypse captures that concern. However, the operational problem reaches beyond the size of the list. A faster flow of disclosures means more decisions about which findings represent a reachable attack and which corrections can actually reach production.
Daily CVE Publications Have More Than Doubled
The change becomes clearer when comparing equivalent periods. From January 1 through November 2, 90,420 CVEs became public in 2026, against 39,680 during the same period in 2025. That represents approximately 128% growth, with the daily average rising from 129.7 to 295.5 publications.
Recent monthly totals also show the acceleration. January recorded 4,302 publications, September reached 14,933, and October added 17,050. These figures describe publication activity, rather than the dates when developers introduced the underlying defects.
Consequently, the increase cannot establish that organizations suddenly acquired the same number of new weaknesses. It does show a much larger volume of disclosed issues to assess. Nor does the trend alone establish how much of that growth came from AI-assisted discovery.
Each Disclosure Can Expand The Assessment Workload
A global CVE total is only the start of an organization’s assessment process. Each disclosure must connect to an actual software component, version or configuration before it becomes a local finding. One relevant record can then affect many hosts, while another may have no match anywhere in the environment.
The next question concerns reachability. For example, a vulnerable management service behind restricted administration access presents a different entry condition from the same service exposed publicly. Credentials, enabled features and network paths can further change what an attacker needs.
As a result, rising publication volume creates work even when many records ultimately fall outside the installed environment. If assessment capacity stays constant, faster intake can build a queue unless matching and prioritization remove irrelevant work. Counting open findings alone does not reveal how many reachable attack paths remain.
Severity Alone Cannot Order The Entire Queue
The CVSS Base score measures technical severity, independently of an organization’s environment and current threat activity. Although CVSS includes Threat and Environmental metrics, sorting only by Base scores leaves those additional dimensions out.
EPSS addresses a different question by estimating the probability of observed exploitation in the next 30 days. Meanwhile, the KEV catalog identifies vulnerabilities with confirmed exploitation in the wild. Neither signal proves that a specific system is vulnerable or compromised.
Therefore, a high global score still needs a connection to a reachable local asset. An exposed service with access to sensitive systems can carry different consequences from an isolated test installation. Under heavier disclosure volume, those differences determine whether a queue reflects operational exposure or merely reproduces the largest severity numbers.
AI Can Turn A Finding Into A Working Exploit
CVE-2026-98432 illustrates the technical stakes behind the growing workload. Concurrent processing of incoming IPv4 TCP connections can free socket-option memory while another path still uses it. Specially timed traffic can then trigger a use-after-free before application authentication becomes relevant.
A laboratory exploit first used an overread to leak a kernel pointer and defeat kernel address randomization. It then reused the flaw to overwrite a callback pointer. When the kernel invoked that callback, a staged payload chained existing functions into a shell command running as root.
The work used an unreleased internal AI research model after initial prompting. Its demonstrated exploit depended on a Multipath TCP listener, although the underlying flaw is not limited to MPTCP. This establishes a concrete exploit-development capability, rather than evidence of criminal deployment or proof that AI caused the entire publication surge.
Patch Readiness Moves At Different Speeds
More disclosures also mean more cases in which a fix has several stages to cross. An upstream correction must reach the relevant distribution or product branch, pass testing and reach affected machines. A released update and a verified running fix represent different states.
The Linux example makes that distinction visible. On November 2, Ubuntu listed fixes for several supported releases in its proposed testing repository, with older supported releases still pending. Its table separately identified Ubuntu 26.10 as fixed. Therefore, one upstream correction did not translate into identical readiness across every supported release.
Amazon Linux had released corrected kernel packages, with a reboot required for the documented update path. However, installing those packages alone does not prove that a host has started the corrected kernel. As the assessment queue grows, closing a finding on package availability alone can conceal remaining exposure.
Virtual Patching Covers Specific Attack Paths
Virtual patching blocks known exploitation attempts without changing the vulnerable code. It can reduce exposure while a permanent correction moves through testing or deployment. However, coverage depends on the enforcement point, inspected traffic and attack variants the rules recognize.
For the Linux flaw, temporary packet filtering can reject incoming IPv4 TCP packets carrying IPv4 options. That addresses the documented network-layer trigger. An HTTP request-body rule examines a later processing stage, so its presence cannot establish equivalent protection for the kernel’s connection handling.
Conclusion: CVE Growth Demands Verified Exposure Reduction
The rise in CVE publications changes the workload long before it changes an organization’s actual exposure. Each relevant disclosure still needs an affected asset, an accountable owner and a decision about urgency. However, processing more records is useful only when that work leads to a measurable change in what an attacker can reach or exploit.
A smaller queue can reflect better filtering without showing that any vulnerable service has changed. Similarly, a completed deployment task can leave the old kernel running. Progress therefore needs evidence tied to the affected system, rather than a count of reviewed advisories or closed tickets.
The Linux example also shows why the enforcement point matters. Application authentication sits too late to protect vulnerable connection handling in the kernel. A temporary network rule and a corrected running kernel address different stages, so their verification must remain separate.
Why This Threat Matters
- Volume increases assessment pressure. When disclosure intake rises, asset matching and ownership become essential to keeping relevant findings from waiting behind unrelated records.
- Reachability changes urgency. An exposed listener can provide an entry point even when the application behind it requires authentication.
- Exploit capability adds context. An AI-assisted laboratory chain demonstrates technical feasibility, but it does not establish criminal use or explain the entire publication increase.
- Release status is incomplete evidence. A distribution can offer a correction while individual machines still run affected code after installation.
- Interim coverage needs an owner. A temporary rule requires a defined traffic path, validation and a review date while permanent remediation proceeds.
Where Defensive Control Must Operate
Xcitium Vulnerability Assessment identifies exposed services, outdated software and weak perimeter configurations through automated scanning and manual validation. Its findings and remediation guidance help teams connect disclosed weaknesses to infrastructure that requires action.
Xcitium Advanced EDR adds continuous monitoring, behavioral detection and response on supported, managed endpoints while remediation proceeds. Its endpoint telemetry and forensic records help teams investigate suspicious activity when exploitation leads to host execution. This complements exposure assessment and patch deployment.
Operational priorities should also reflect exploitation evidence, exploit probability and the consequences of access to each affected service. When a correction cannot yet run, restrict the reachable path and validate any interim protection at the layer handling the trigger. Keep that protection visible as temporary coverage until the permanent fix is verified.
Make Closure Reproducible
For each urgent exposure, record the affected service, the responsible team and the evidence required for closure. After deployment, verify the active software or kernel and recheck the service from the relevant network position. If a temporary rule remains necessary, document its scope, persistence and next review. Track how long high-priority reachable exposures remain open, alongside ticket throughput, so reporting shows which attack paths changed and which still require work.