
Don’t Fear the Unknown. Contain it.
Latest Blogs
- HOOKEDGE: APT28 Hides C2 Traffic Inside Microsoft Edge
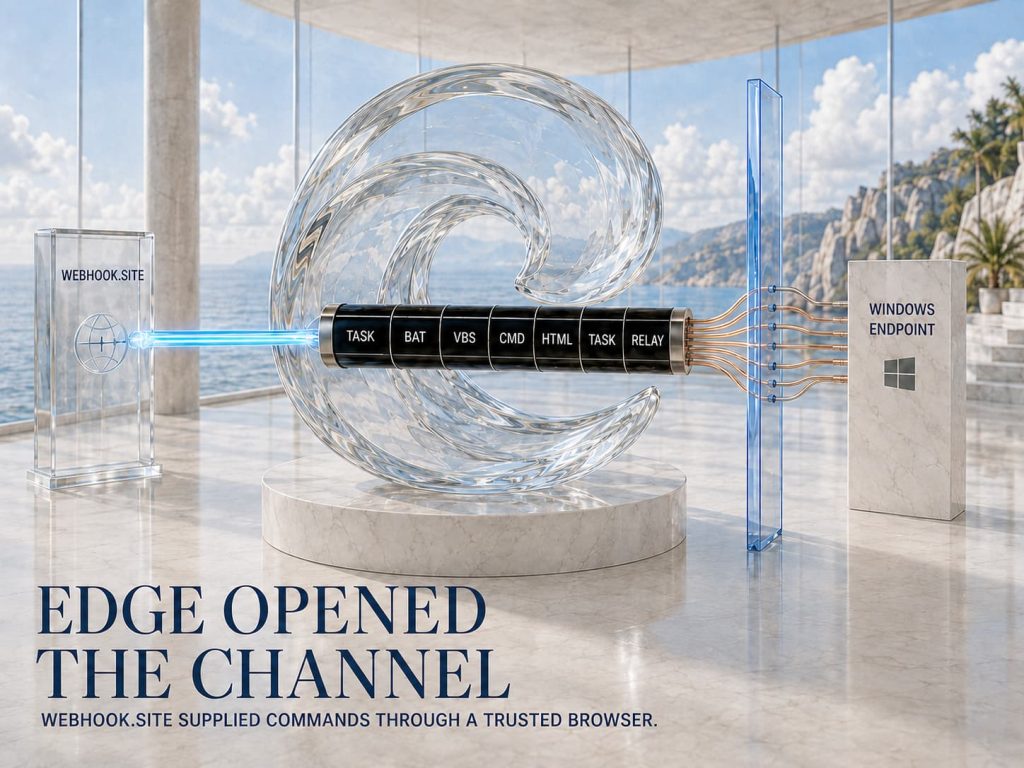 An agenda for a meeting pops up, seemingly from a government ministry. This document prompts the user to… Read more: HOOKEDGE: APT28 Hides C2 Traffic Inside Microsoft Edge
- miniOrange SAML Flaw Lets Anyone Log In as WordPress Admin
 Your scanner indicates that the plugin is already patched. There is no new update available according to the… Read more: miniOrange SAML Flaw Lets Anyone Log In as WordPress Admin
- WordlistLoader and SynkLoader Target Windows Credentials
 An invitation comes through from the company IT help desk. The message invites you to download a utility… Read more: WordlistLoader and SynkLoader Target Windows Credentials
- Zimbra RCE Flaw Under Active Attack, CISA Sets Deadline
 Today, over 12,000 Zimbra mail servers are openly accessible on the Internet, and the attacker knows which SNMP… Read more: Zimbra RCE Flaw Under Active Attack, CISA Sets Deadline
- Medusa 2026: The Ransomware Stage Begins After Identity and Remote Management Are Lost
 The latest Medusa federal advisory outlines an easily replicable chain of events leading from initial access through enterprise-wide… Read more: Medusa 2026: The Ransomware Stage Begins After Identity and Remote Management Are Lost
- Heights Finance Breach Exposes 1.2 Million People
 On May 7, Heights Finance identified a situation where a person accessed a cloud platform which housed their… Read more: Heights Finance Breach Exposes 1.2 Million People
- Ransomware on vCenter May Be a Cover, Not the Goal
 When hackers were exploiting the severe vulnerability in VMware vCenter, they were busy creating administrator accounts and backdoor… Read more: Ransomware on vCenter May Be a Cover, Not the Goal
- A 2014 Certificate Still Loads Kernel Rootkits in 2026
 The digital signature which authenticates this rootkit has expired as of September 2014. It had been obtained the previous… Read more: A 2014 Certificate Still Loads Kernel Rootkits in 2026
- Eight AI Agents Breached 21 Government Systems in Four Days
 The hackers did not discover any new vulnerabilities. Rather, they discovered that there was one government website that… Read more: Eight AI Agents Breached 21 Government Systems in Four Days
Why Choose Xcitium?
Xcitium exists to ensure that people can embrace technology fully, without the shadow of insecurity hanging over them.
We’re here to give users the freedom to explore, create, and connect without fear. Whether it’s preventing unknown files from compromising systems or offering innovative approaches to endpoint protection, Xcitium’s technology is designed to foster confidence.
We believe that by keeping the digital ecosystem secure, we’re directly contributing to human evolution—by enabling people to take full advantage of the tools that define our era.

“We selected Xcitium and its Advanced Endpoint Protection solution because it clearly addresses the problem of malware and cyber-attacks through a unique containment technology. Also, its prevention philosophy is different from anything else in the market today.”
Wade Warrenberg