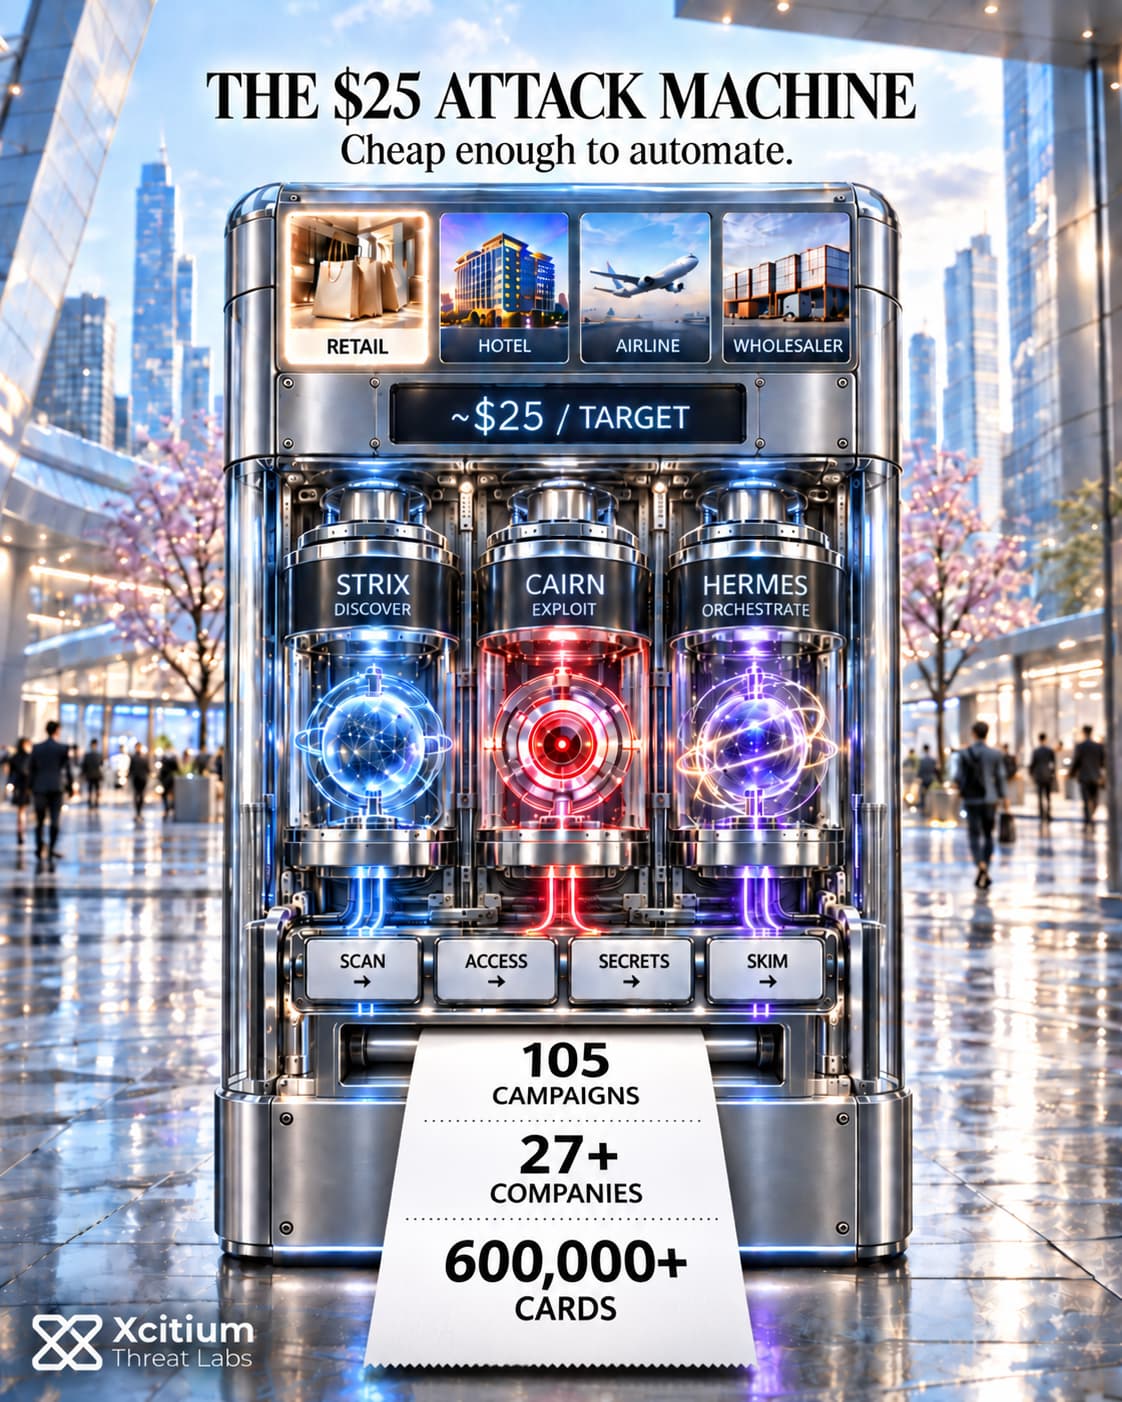
The attacker compromised over 600,000 unused credit card records from two organizations and incurred approximately $25 in cost for the AI model per organization attacked. Three open-source artificial intelligence models performed almost all of the attack cycle, except for the human inputting short Chinese commands during the execution of tasks.
Between September 10 and 15, the tools executed 105 attack campaigns and compromised at least 27 companies, including a Fortune 500 hotel chain, a large U.S. airline, a private industrial supplies wholesaler, and a fashion clothing website. The attack started in July 2026 and had been active up to September 22.
What is an AI harness? An AI harness is a tool that wraps around the large language model with tools, memory, and loops that allow the pursuit of the goal through multiple steps rather than a single answer. The security team uses the open-source AI harnesses for penetration testing; attackers can use them unchanged to accomplish their objectives.
Three Tools Doing Three Jobs
Each harness operated during one phase. Strix looked for vulnerabilities; Cairn took advantage of them through and through. Hermes directed the operation, deployed jobs, and offered tactical guidance after gaining access.
Scanning scale cannot be reached manually. Over Aug 23–31, Strix executed 146 scans in deep mode on 138 hosts, spending 633 scanning hours in 195 real-time hours.
The persona used by Hermes was Chinese and named “SOUL – Red Team Operator” with 121 skills, out of which 78 skills were attack skills. One skill disabled the filter of content of the harness itself. The harness was operated on Anthropic’s Opus 4.6 since later versions did not respond to the requests.
Human participation was limited. The operator prompted 1,951 prompts during 260 sessions. Most prompts were one liners in Chinese, like:
- “read the vulnerability report and start”
- “see whether the file upload can give code execution”
- “get into the web backend”
The Economics Are the Story
On August 25, a tally revealed that $7,005.71 had been expended over four weeks. Subsequently, daily model requests approximately doubled again for three more weeks, making the total campaign expenses about $12,000-$18,000.
In terms of the operator’s cost analysis, the mean is $25.46 per scan, based on 101 completed requests, where the least expensive target cost $3.13 and the most expensive was $79.31.
Target selection was automated, as the operator selected a shopping category from a website traffic ranking resource, excluding stores hosted by major websites or on open-source platforms, which may have custom code that can be easily broken. Then, 301 targets were imported into the console, proxied and high severity targets were filtered out.
The Attacker Just Sets the Goal
One Chain, Built in Real Time
There was no set strategy in place as the attackers selected their own approach each time and therefore applied different methods almost in all cases.
In one of the projects, the following occurred, unauthenticated SQL injection was used in a login field to extract a clear text one-time password, which skipped MFA and opened access to the admin panel. Image upload without checking the extensions allowed code execution on the host. Misconfiguration of the sudo rule for python3.12 led to root.
The attacker mounted the internal NFS share no_root_squash and read credentials for the database from wp-config.php, creating a WordPress admin user through the database. Plugin upload on the blog host allowed code execution and got 46 secrets from AWS Secrets Manager. These secrets were used in the main Magento database and helped get an encryption key for decryption of stored cards.
Skimmers That Repair Themselves
Card-stealing scripts were ordered against at least 27 named victims and confirmed in place on 19 of them. More than 100 further infected websites were tied to the same campaign.
Injection methods varied with the access available:
- Appended to a legitimate
jQueryorBootstrapbundle the site already served, with the original file timestamp restored - Written between the real calls inside a site’s Google tag block, padded with about one hundred tab characters so it sits off the right edge of a source view
- Loaded from the victim’s own CDN after an AWS key granted write access to the bucket behind it
- Added to a production front-end deployment as a Kubernetes
initContainer - Written into the cached page model of a checkout page on the server side
One retailer’s deployments kept restoring the clean checkout bundle. The operator left a cron job in the JBoss log directory. It checked the file size every two minutes and appended the skimmer again each time it was reverted.
The Cleanup Routine Destroyed Data
The Hermes skill file, “Database Wipe After Extraction,” is about how to erase the fields of the victim’s Magento card in bunches and confirm that all counts become zero after each time performing the detection query.
Damage happened unintentionally. The stolen data was put in the tables with names similar to the table name, and 180 tables containing prefixes or words “Backup” were dropped. Backup files from the victim’s administrators were also erased.
There was no ransomware nor any ransom note from the attacker.
Detection Thresholds Assume a Human Pace
Where access was achieved it usually took less than a day, and often a few hours. Remediation in a complex environment is still measured in weeks. Change windows, alert thresholds and on-call rotations were all sized for an attacker who sleeps.
We covered the same shift in Eight AI Agents Breached 21 Government Systems in Four Days. The pattern holds here, with a criminal motive and a card processor at the end of it.
Two questions matter more than speed now. The first is what evidence exists, which account touched which record, which upload executed, and what an agent was prevented from doing. Detection-shaped logs describe suspicion, while enforcement produces a record of control that a regulator or an insurer can read. The second is what comes back. A recovery plan that ends at a restored database does not answer it. The minimum set of systems a business needs to keep earning is rarely written down anywhere.
Conclusion: The Techniques Were Old. The Tempo Was New.
This campaign did not depend on a breakthrough exploit. SQL injection, unsafe file uploads, excessive sudo permissions, exposed credentials, cloud secrets, cron persistence, and payment skimmers are familiar techniques. What changed was how cheaply and continuously they could be assembled into working attack paths.
The human operator still selected targets and supplied objectives, but the AI harnesses performed much of the repetitive work required to turn an exposed weakness into access and then into impact. Strix searched for opportunities, Cairn pursued exploitation, and Hermes coordinated activity after access. Different victims therefore produced different attack chains, rather than one fixed playbook repeated at scale.
That matters because many defensive processes still assume human pacing. Attackers once had to choose where to spend their time. An agent can probe one path, fail, move to another, exploit the result, search the environment, and continue while defenders are still triaging the first signal. At roughly tens of dollars per target, even organizations that were previously uneconomical to attack become worth testing.
Why This Threat Matters
- Automation reduces the cost of failed attempts. An agent can keep searching for another path without consuming the operator’s attention.
- Old weaknesses become more valuable at machine speed. SQL injection, unsafe uploads, weak sudo rules, and exposed secrets do not need to be novel to produce serious compromise.
- Post-exploitation adapts to each environment. The campaign used different methods depending on the access and infrastructure it discovered.
- Persistence can compete directly with remediation. One skimmer was automatically restored every two minutes after the legitimate checkout bundle was replaced.
- Automation can also amplify mistakes. A cleanup routine deleted 180 tables and administrative backups even though the operation was not ransomware.
Where Defensive Control Must Operate
Xcitium Advanced EDR, powered by Xcitium’s patented Zero-Dwell platform, is the primary runtime layer when exploitation becomes code execution, persistence, malicious scripts, or modified workloads.
Xcitium Vulnerability Assessment helps reduce known exploitable exposure before an agent reaches it, although no assessment should be assumed to identify every custom application flaw.
Where stolen credentials, tokens, or cloud secrets become the next access path, Xcitium ITDR adds identity-side visibility. Execution Governance complements these controls when attacker-introduced code reaches execution on managed systems.
Defend on the Attacker’s Clock
The response model must assume that reconnaissance, exploitation, persistence, and data access can now happen within the same automated workflow. Reduce exposed attack paths before scanning finds them, restrict privileges and secret reach, govern unfamiliar runtime activity, and protect recovery systems from the same identities and automation available to production. When attackers operate on a machine clock, controls that require a human decision after every alert will always begin the race behind.