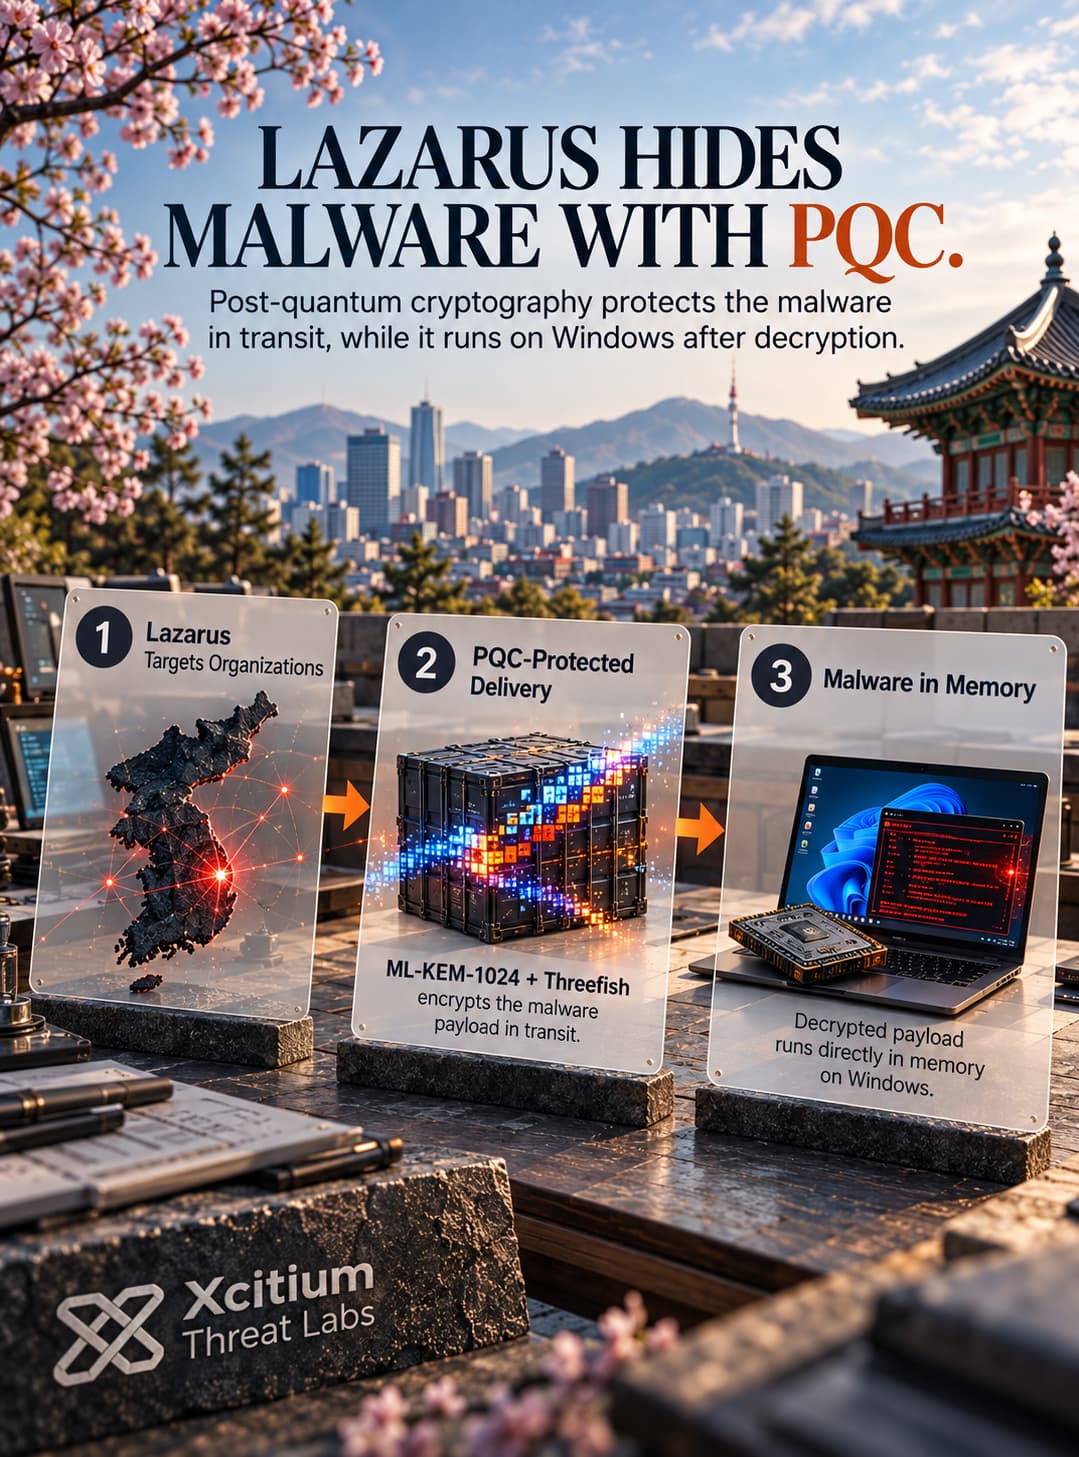
Lazarus is using post-quantum cryptography to conceal malware delivery in an espionage campaign targeting South Korean organizations. The operation, FlashHole, combines encrypted payload exchanges with a Windows infection chain that runs largely in memory. Its tools can collect browser credentials, inspect files and give operators remote command capabilities.
The October 21, 2026 disclosure identifies at least three affected organizations across software, construction and wired communication equipment manufacturing. However, the earliest evidence reaches back to July 2025. That timeline describes an established operation, rather than an attack that began with this week’s disclosure.
Lures Match The Victim’s Work
A developer’s resume and an interior design portfolio supplied two different reasons to open the malicious pages. The subjects fit the targeted industries, so the links could arrive as ordinary work material. Both sites pulled in external JavaScript.
The likely route to those sites was a targeted phishing email. However, the investigation could not reconstruct the exact event that started infection. It also couldn’t establish how the attackers abused CrossWeb EX, a local financial security application.
That leaves a break in the reconstructed sequence between browsing and the observed Windows activity. The report does not identify a specific zero-day for that step. Nor does it show that every computer with the application would become infected merely by opening the page.
A Security Process Starts The Windows Chain
In the observed Windows sequence, the CrossWeb EX process launches fsquirt.exe, a legitimate Windows executable. Shellcode injected into that process carried TechHub, a downloader that retrieved further malware from private repositories on a software development platform.
As a result, the initial activity crossed several familiar boundaries. A browser opened a relevant-looking page, a security application started a Windows program, and a development service carried additional payloads. Each component had a legitimate purpose outside this chain.
Yet those familiar components do not establish permission for the code running through them. The meaningful relationship is between the originating process, the injected payload and its subsequent actions. Looking at the executable name alone would describe only the host program.
Post-Quantum Keys Protect The Next Payload
LPEClient now gets its incoming payloads through ClientHub, with ML-KEM-1024 contributing to the key exchange. The shared secrets become key material for Threefish. That cipher decrypts a response containing parameters and Cubridge, which LPEClient loads into memory.
ML-KEM-1024 belongs to a key encapsulation standard finalized in August 2024. Its job is to establish a shared secret over a public channel; symmetric cryptography can then use that secret to protect data.
The post-quantum label refers to resistance against attacks that future quantum computers might enable. However, nothing in this exchange requires the attackers to possess such a computer. Using a standardized algorithm also says nothing about whether the software deserves trust.
Once decryption finishes, the backdoor still needs to run. Consequently, encrypting its journey to the machine and carrying out its instructions remain separate steps. The cryptography conceals delivery without eliminating the endpoint activity that follows.
Persistence Rebuilds The Memory Chain
FlashHole’s operators didn’t leave everything in memory. TouchHub writes files and registers a Windows service, providing a way to start TouchShift through DLL side-loading. That loader brings another TechHub instance into memory.
From there, TechHub deploys ClientHub and LPEClient. The chain appears designed to bring Cubridge back after persistence is in place, although that purpose remains an assessment.
This is why the initial memory-only stage cannot describe the whole intrusion. A running copy of the backdoor and the components that can reload it have different lifetimes. Removing the process would leave the service question unanswered; finding a few files would reveal only the parts written to disk. Neither observation, by itself, accounts for every stage.
The Backdoor Can Reach Files And Browser Sessions
With Cubridge in place, operators can issue commands, inspect files, take screenshots and load more code. Tools targeting Chromium-based browsers add passwords, cookies and browsing history to that set of capabilities. Those are access paths into a working computer, with different consequences for the person using it.
For example, a password can remain useful beyond the current browser session. A session cookie may instead connect the theft to activity that already passed a sign-in check. Neither item proves that the attacker successfully entered a particular external account.
The published analysis describes what these tools can do, but it doesn’t provide a complete list of documents taken from the victims. Nor does the minimum of three identified organizations settle the campaign’s total size. The investigation establishes a minimum footprint, with the full extent still unknown.
Conclusion: Encrypted Delivery Still Ends In Endpoint Execution
FlashHole links a financial security process to a legitimate Windows executable hosting injected code, followed by encrypted payload exchanges. Process ancestry and subsequent resource access give defenders concrete evidence to investigate. The security application’s expected role does not authorize injected code, while the reputation of a delivery service cannot establish a payload’s purpose. Malicious code crosses the critical boundary when it gains authority over endpoint resources.
ML-KEM contributes shared secrets to the payload encryption scheme. After decryption, however, the payload still loads into memory and performs operations on the host. That creates a practical investigation path even when network content remains opaque. The unresolved initial trigger limits conclusions about the exploit, but it does not erase the observed execution and persistence stages.
Why This Threat Matters
- A security dependency becomes an execution path. CrossWeb EX sits between routine website access and native software, so defenders must scrutinize unexpected child processes.
- Process reputation offers incomplete evidence. A legitimate Windows executable can host injected code, making its behavior and ancestry essential to an investigation.
- Modular delivery extends the investigation. Separately loaded components mean that identifying one payload does not establish which other capabilities reached a particular host.
- Persistence outlasts a process. Malicious file and service artifacts require separate remediation because stopping the current process leaves their ability to restart code unresolved.
- Browser theft creates a conditional identity risk. Password and cookie collection capabilities justify account review, although successful reuse requires its own evidence.
Where Defensive Control Must Operate
Xcitium Advanced EDR, powered by Xcitium’s patented Zero-Dwell platform, provides endpoint monitoring, behavioral analysis and response on supported, managed Windows systems. In this campaign, those capabilities are relevant to investigating unexpected process launches, injected payload activity and unauthorized persistence. Correlating these events can help establish the sequence behind an apparently ordinary executable.
Execution Governance complements that visibility by restricting unknown code’s access to real endpoint resources before trust is established. Its role belongs at applicable native execution stages. A trusted process hosting injected code still requires behavioral scrutiny, and the undisclosed browser-to-process transition needs separate investigation. Teams should verify enforcement on their deployed agent and policy configuration, including the relevant loader behavior.
Verify Recovery Beyond The Running Process
Response teams should preserve volatile evidence before disruptive cleanup where feasible, then investigate the loader chain and service-based restart path together. For example, validating the service configuration and associated files can expose a route that process termination misses. Where browser-data access is suspected, review affected accounts and revoke exposed sessions as appropriate. Recovery should include checking for renewed payload activity after remediation, while documenting which persistence components and access paths the investigation actually ruled out.