Targeted advertisements delivered Candiru spyware to devices at Al Jazeera, turning ordinary ad placements into an espionage channel. The technique, called AdFection, requires no click on the advertisement. Rendering it can start the sequence that selects a device and delivers the attack.
The delivery infrastructure connects to Discover-Tech, an Israel-based advertising company serving commercial surveillance partners. Public technical evidence released on October 15 documents the Al Jazeera attacks during 2024 and 2025. However, the governments buying these capabilities remain unidentified.
An Advertising Auction Supplies the Entry Point
A visit to a website or an app can trigger an auction for an advertising slot. Through real-time bidding, a buyer receives information about the opportunity and submits a bid with a proposed advertisement. If the bid wins, the advertising system places that creative.
This exchange is part of the advertising system’s normal operation. However, the same process gives a hostile buyer access to a device through infrastructure that the publisher already uses.
The publisher’s article or app does not need to contain an attacker-written story. Instead, the advertisement carries the initial connection into the delivery chain. Consequently, selecting a reputable publication does not establish the trustworthiness of every external component that loads beside its content.
The Server Selects Who Receives More Code
Discover-Tech’s targeting platform supports identifiers including an IP address or advertising ID. Its advertisements contact a server that decides whether to return more code. Selected devices receive additional JavaScript; most other recipients receive no further code from that server. Nevertheless, an ordinary-looking ad can still collect information from the recipient.
This selection creates a difference between the visible advertisement and the code a particular device receives. A scanner revisiting the placement may therefore encounter a different response. The targeting decision happens after the advertisement has already reached its audience.
Technical analysis of the staging code also describes encrypted communication and instructions arriving from remote infrastructure. The code can gather device characteristics and execute additional JavaScript within its browser context. However, browser script execution and native spyware installation remain separate stages. A script running in an ad frame does not automatically gain unrestricted access to the operating system.
Al Jazeera Logs Connect Advertising to Infection
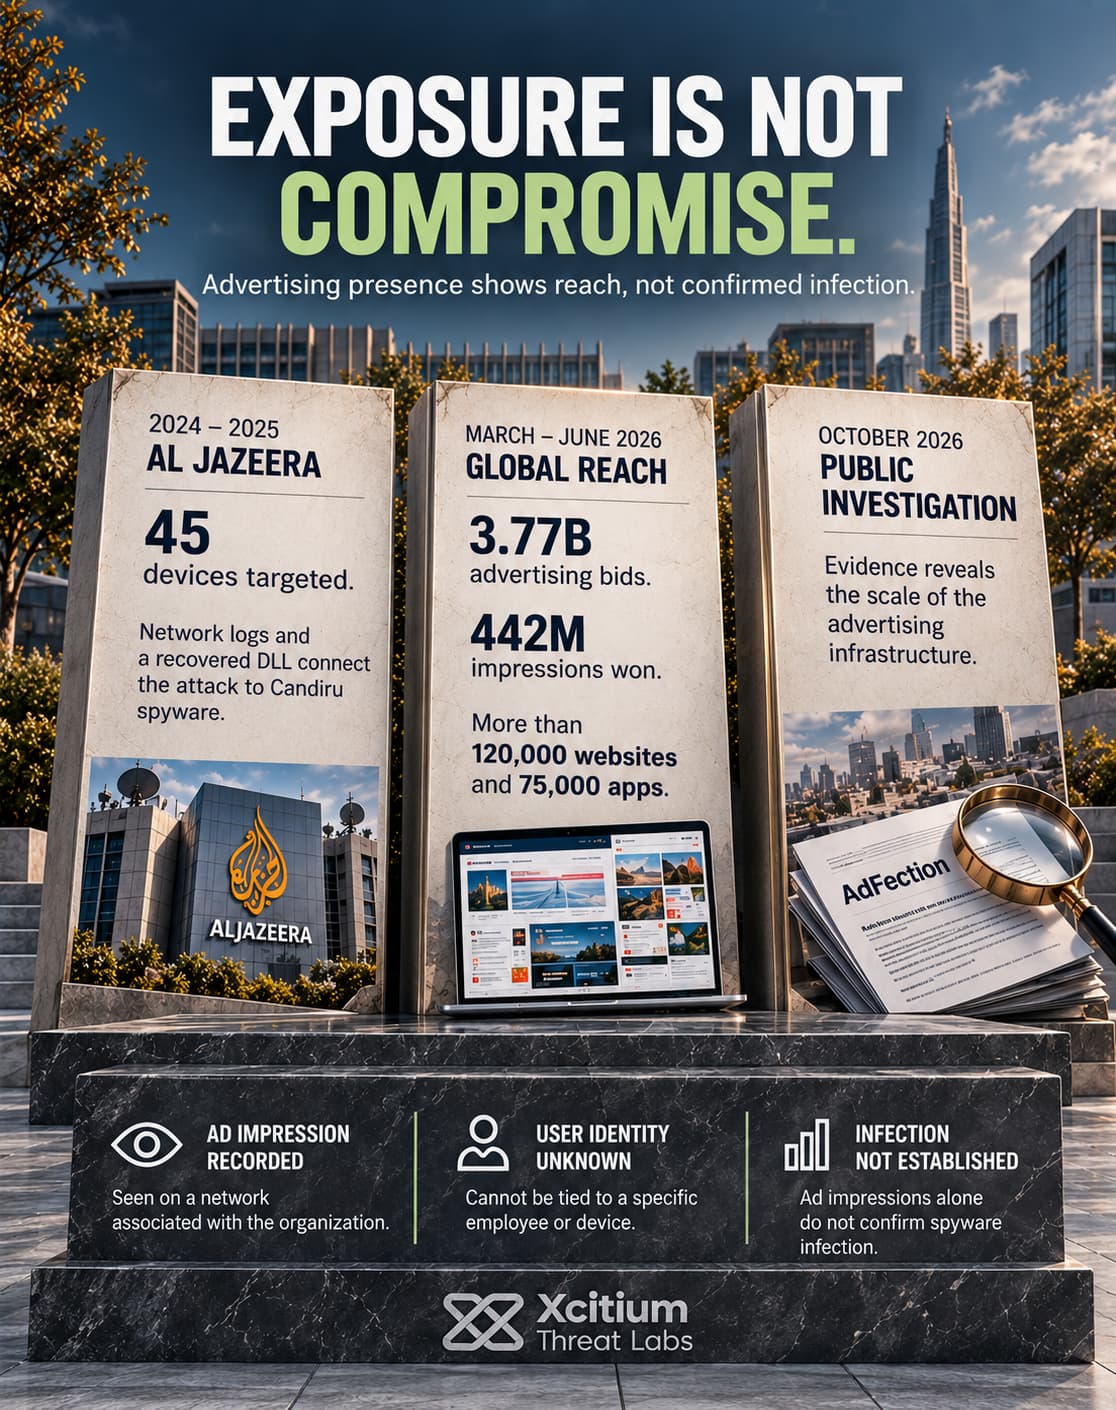
Discover-Tech advertisements targeted at least 45 Al Jazeera devices during 2024 and 2025. The broadcaster supplied network logs that record infected devices contacting the ad infrastructure, a Candiru validation server, and finally command-and-control servers.
Al Jazeera also isolated a dynamic-link library (DLL) from a compromised device. Together, the code similarities and network infrastructure support the Candiru attribution with high confidence. This evidence reaches beyond an advertisement appearing on a screen; it connects the delivery channel to an installed spyware payload.
However, the 45-device figure describes targeting. It doesn’t give a complete count of successful infections, and the recovered sample cannot establish compromise of every mobile platform in the advertising records.
The separate analysis of staging code also leaves part of the exploit chain uncaptured. Consequently, there isn’t enough public evidence to name a single browser flaw or patch covering every delivery path.
Profiling Extends Beyond the Infection Targets
From March through June 2026, Discover-Tech’s ad-buying platform submitted bids for approximately 3.77 billion advertising impressions. It appeared to win about 442 million. Ads containing the relevant script tags ran across 75,373 mobile apps and 120,768 websites.
Those are distribution figures, so they describe where the ads appeared rather than how many devices carried spyware. The Al Jazeera infection evidence covers a much narrower set.
Meanwhile, the staging analysis documents publisher-cookie collection in some advertising contexts. An ad frame’s relationship to the publisher determines which cookies its scripts can access. Cross-origin rules still apply, and ordinary JavaScript can’t read HttpOnly cookies.
Profiling therefore deserves attention in its own right. A device can disclose characteristics or identifiers without reaching the spyware installation stage. Likewise, the billions of bidding opportunities don’t represent billions of attempted infections.
Sensitive Networks Also Received the Advertisements
Advertising records place Discover-Tech impressions inside networks associated with NATO, the United Nations, European institutions, and national government bodies. The reach also extends to critical infrastructure and semiconductor companies.
An impression on an institutional network does not identify the person behind it. For example, a shared exit point or guest connection can associate traffic with an organization without establishing an employee’s identity. Nor does the record alone establish that the server selected that device for infection.
Even with those limits, the exposure has an international security dimension. Advertising infrastructure can reach people inside sensitive organizations without an operator first compromising the organization’s own public website. The relevant entry point may sit in an unrelated site or application that a device loads while using that network.
Vendor Approval Preceded Removal From Ad Platforms
Major advertising platforms and an industry vendor registry had listed Discover-Tech as an approved participant. That approval placed the company inside the advertising system, where its servers could supply additional code after an ad loaded.
Following the investigation, advertising intermediaries blocked Discover-Tech’s access. The industry registry also suspended the company from its vendor list. These removals cut off documented routes to advertising inventory.
Those actions address Discover-Tech’s access through the affected services. They don’t establish that advertising-based spyware delivery has stopped across the market. The analyzed records cover one ad-buying platform over four months; the investigation also documents relationships with other advertising intermediaries.
Conclusion: The Ad Was the Attack Surface
AdFection demonstrates how the digital advertising ecosystem can become a delivery channel for targeted spyware without requiring victims to click a malicious link, open an attachment, or visit an attacker-controlled website. By exploiting legitimate advertising infrastructure, Discover-Tech enabled surveillance operators to reach selected devices through ordinary advertisements displayed inside websites and applications.
The attack begins with a routine advertising transaction. When an advertisement is rendered, its embedded code contacts remote infrastructure that determines whether the device matches a target. Selected devices can receive additional JavaScript and proceed toward further exploitation, while others may receive no additional payload. This selective delivery makes malicious activity difficult to reproduce through conventional scanning.
The investigation connects this technique to Candiru spyware infections at Al Jazeera. Network logs showed the progression from advertising infrastructure to spyware validation and command-and-control servers, while a recovered DLL provided additional evidence of an installed payload.
The broader danger lies in the infrastructure itself. Discover-Tech’s advertisements appeared across more than 120,000 websites and 75,000 mobile applications. Those figures demonstrate distribution, not infection. They nevertheless reveal how widely surveillance infrastructure can operate inside an advertising system that publishers and users routinely trust.
Why This Threat Matters
- No user interaction is required. Simply rendering an advertisement can initiate targeting and potentially lead to spyware delivery.
- Legitimate advertising infrastructure becomes an entry point. Attackers can reach devices through reputable websites and applications without compromising those publishers.
- Selective payload delivery complicates detection. Malicious code is delivered only to chosen devices, making repeated scans less likely to reproduce the same behavior.
- Advertising exposure enables surveillance beyond malware installation. Device identifiers, characteristics, and accessible browser data can support profiling even when spyware is not deployed.
- Approved vendors are not automatically trustworthy. Discover-Tech operated within established advertising networks before its access was revoked.
- Advertising reach does not equal infection. Hundreds of millions of impressions cannot be treated as confirmed compromises.
Where Defensive Control Must Operate
Xcitium Advanced EDR, powered by Xcitium’s patented Zero-Dwell platform, provides an important endpoint defense layer against malicious code execution, suspicious process behavior, spyware persistence, and command-and-control activity on supported systems.
Execution Governance adds protection where untrusted executable code reaches an enforceable endpoint boundary. However, browser-level JavaScript execution and native spyware installation are distinct stages, and the undisclosed exploit chain prevents claims of guaranteed prevention against this specific attack.
Stop Malicious Advertising Before It Reaches the Endpoint
Organizations should treat third-party advertising infrastructure as an external code-delivery surface, not merely a marketing or privacy concern. Blocking unnecessary advertisements and tracking requests on managed devices and network gateways reduces exposure before malicious content can reach the browser or application.
Security teams should also review advertising-related network traffic, investigate connections to known surveillance infrastructure, and correlate suspicious browser activity with subsequent endpoint and command-and-control communications. Advertising identifiers should be restricted where possible, particularly on devices used by journalists, government personnel, and other high-risk targets.
The removal of Discover-Tech from major advertising platforms addresses documented infrastructure but does not eliminate the underlying technique. Effective defense requires reducing unnecessary exposure to executable advertising content and enforcing independent security controls when untrusted code reaches the endpoint.